A security assessment can contain accurate observations and still fail to produce change. Property ownership and executive leadership need more than a list of vulnerabilities. They need a clear explanation of business impact, priorities, options, cost considerations, responsible parties, and how improvement will be measured.
Begin With an Executive Risk Summary
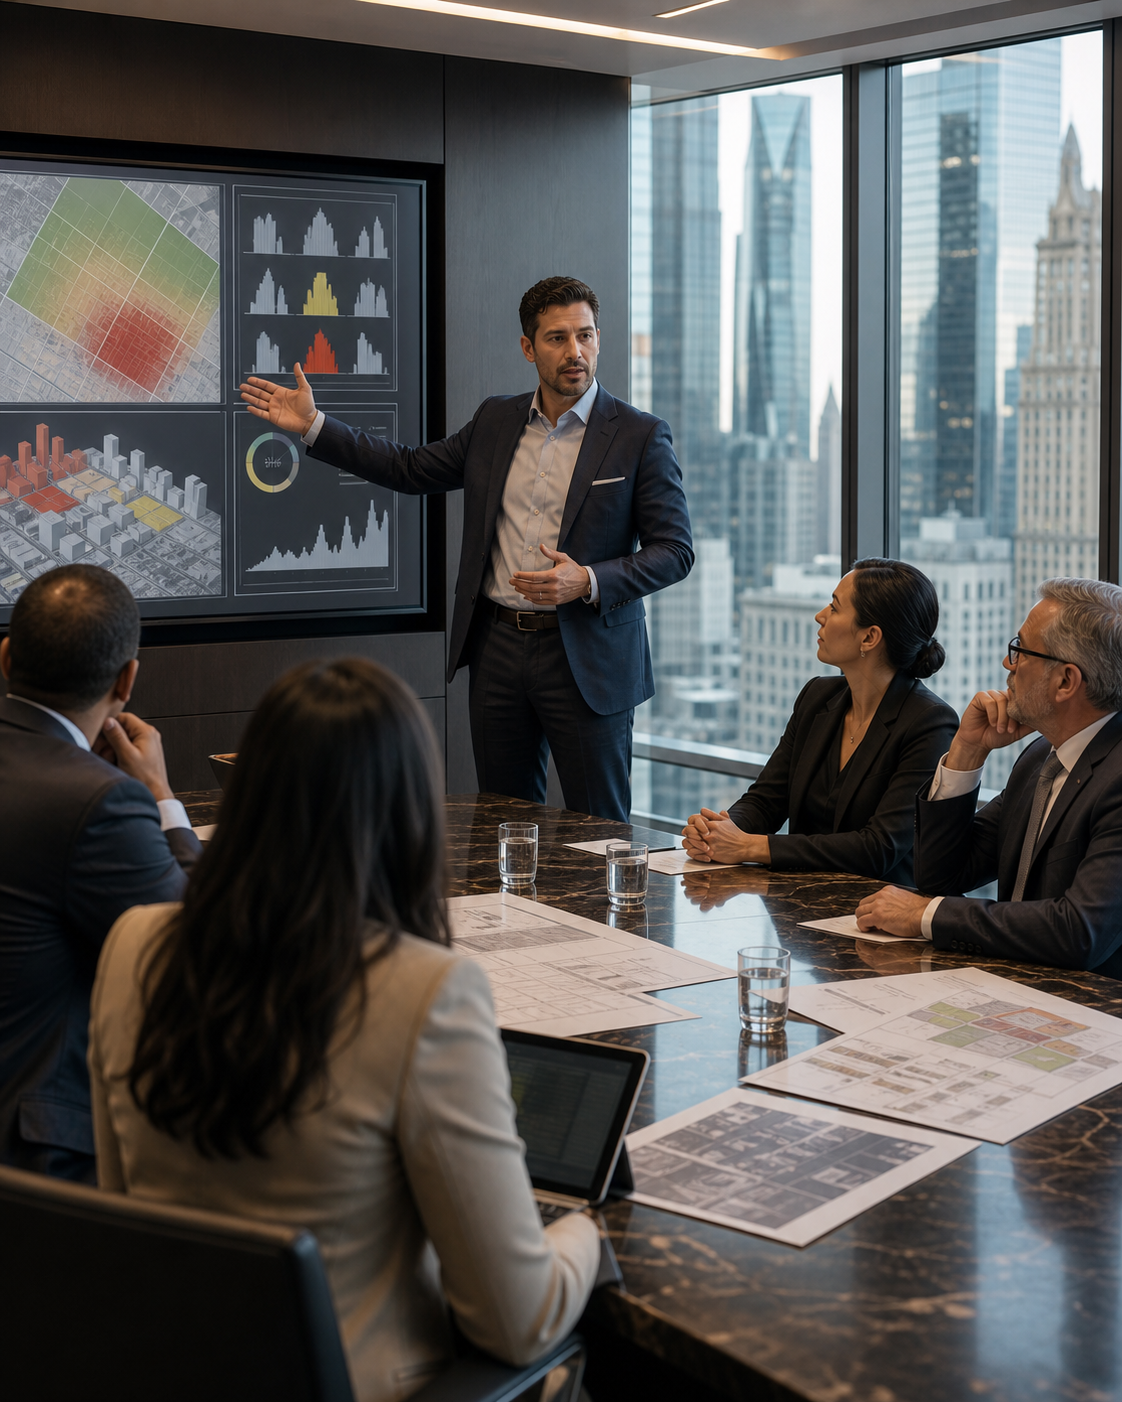
The opening section should explain the most important exposures in plain language. Leadership should understand what could happen, why the existing controls may be insufficient, which operations could be affected, and what requires immediate attention.
Separate Findings From Recommendations
A finding describes the condition supported by evidence. A recommendation explains what should change. Keeping them separate helps decision-makers understand why an investment is being proposed and prevents conclusions from appearing unsupported.
Prioritize by Consequence and Likelihood
Not every issue deserves the same urgency. A blocked emergency exit, uncontrolled master key, or failed entrance lock may require immediate action. A camera upgrade or lobby redesign may belong in a planned capital project. Prioritization helps leadership allocate attention and funding.
Present Practical Options
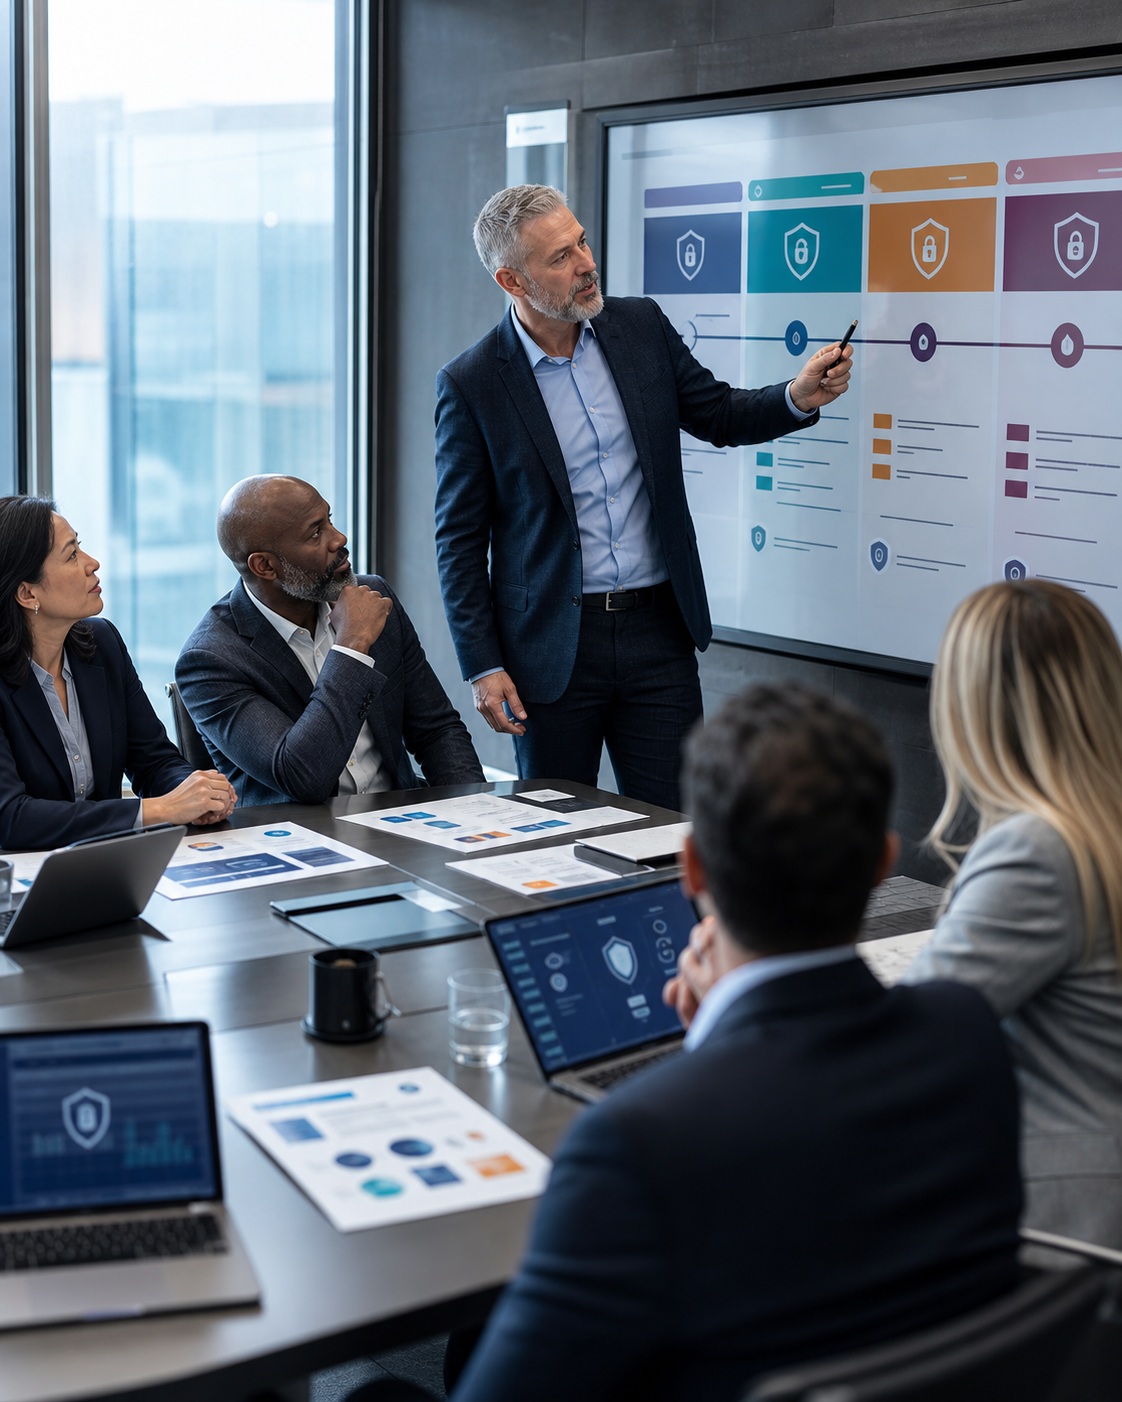
Some risks can be reduced in several ways. Leadership may compare a staffing adjustment, access-control change, physical barrier, training program, or procedural solution. The report should explain advantages, limitations, dependencies, and ongoing operating requirements.
Assign Ownership and Dates
Every accepted recommendation should have an accountable owner, target date, and completion evidence. Tasks may belong to security, property management, engineering, human resources, IT, tenants, or ownership.
Include Quick Wins and Long-Term Projects
Low-cost corrections such as updated contacts, revised visitor rules, door repairs, post-order changes, or targeted training can begin while larger improvements are budgeted.
Use Evidence Leadership Can Verify
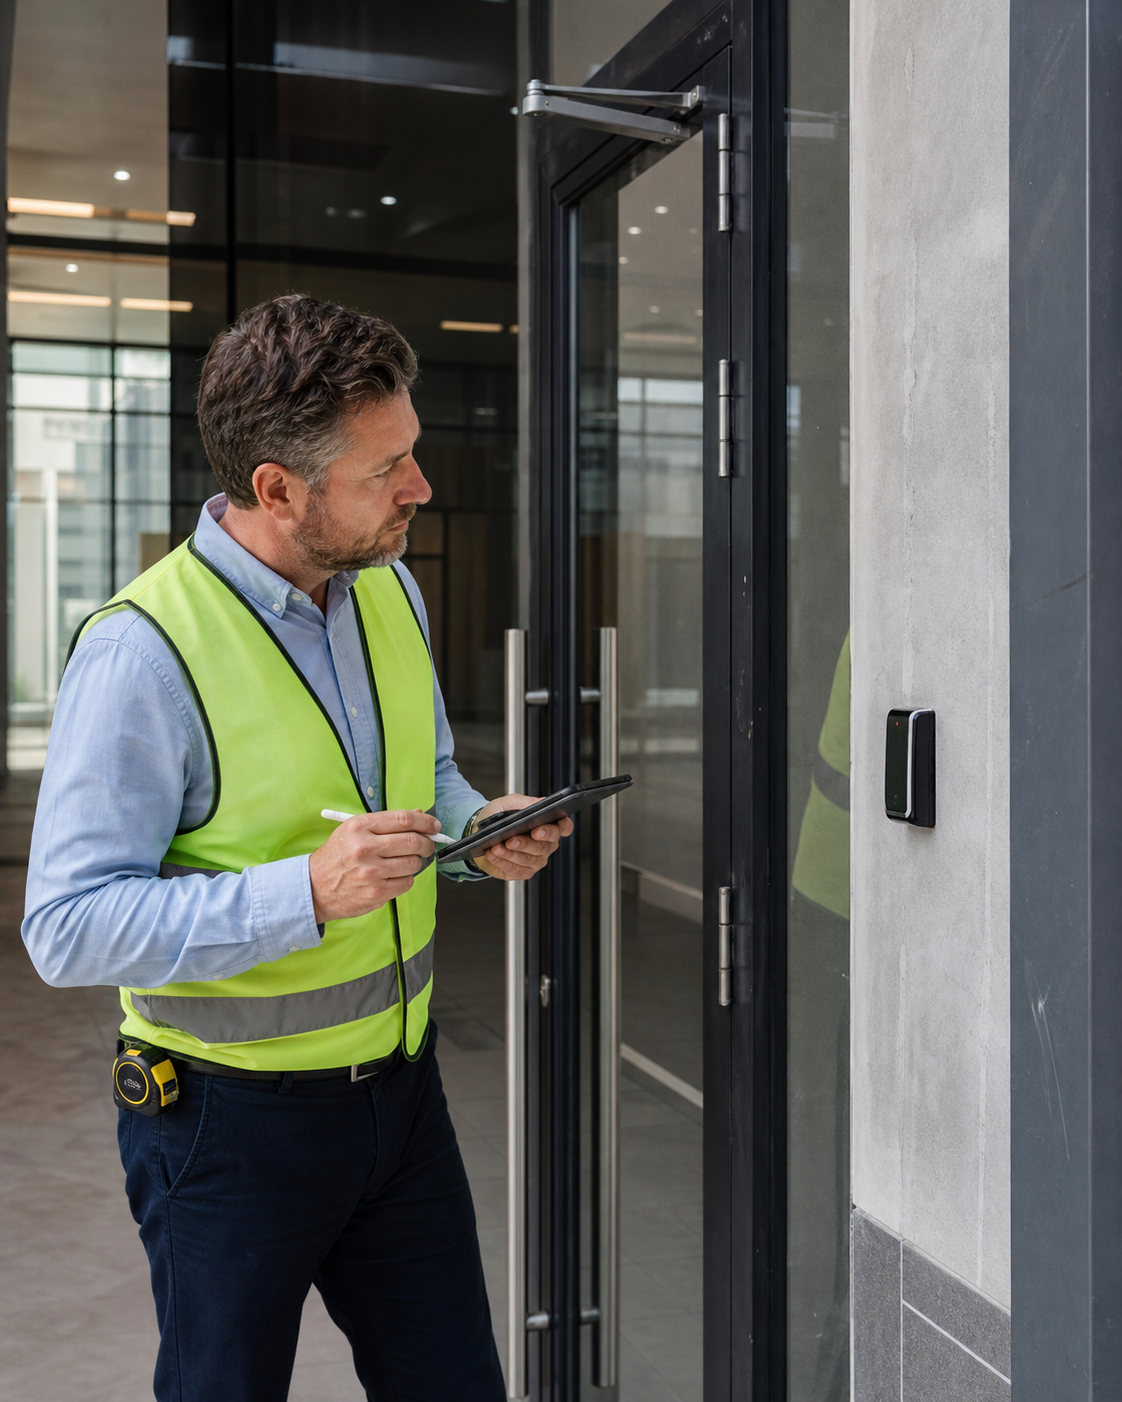
Photographs, incident patterns, access data, patrol results, observations, interviews, and documented tests provide a defensible basis for decisions. Sensitive information should be handled carefully and shared only with authorized stakeholders.
Schedule a Follow-Up Review
A report is not complete when it is delivered. A follow-up should confirm completed work, evaluate remaining exposure, and identify recommendations that need adjustment.
Turn Findings Into Action
Guardian ISI provides site-specific New York security assessments that connect operational details to management decisions. Call or text (212) 602-1695 or request coverage.
A decision record leadership can use
| Field | What to record |
|---|---|
| Evidence | The observed condition and supporting record |
| Impact | The people or operations exposed |
| Decision | Approved action and funding, or the reason for deferral |
| Owner and date | Responsible person and target completion |
| Verification | How completion will be checked |
Move from review to follow-through
- Confirm the facts with the responsible property team.
- Present prioritized decisions to leadership.
- Assign accepted actions and review their completion.
Frequently asked questions
What should an executive security summary contain?
Main risks, consequences, urgent actions, strategic options, and decisions required.
Should the report include cost estimates?
Include reliable ranges or assumptions when available and identify items requiring vendor pricing.
Who should own corrective actions?
The leader or department with authority and resources to complete them.
How is completion verified?
Through inspection, documentation, testing, records, or other defined evidence.